Quick answer: A homomorphic encryption example is any case where one party computes on another party’s data without ever seeing it in plain form. The clearest homomorphic encryption examples in production today are running a machine learning model on encrypted inputs, querying a database without revealing which record you searched for, and combining several organizations’ data sets into one shared analysis without anyone exposing their raw records. Hospitals, banks, and government agencies already run versions of all three.
Homomorphic encryption is one of several privacy enhancing technologies (PETs), and it stands out because it allows computation directly on encrypted data. Nothing needs to be decrypted first. The result comes back encrypted too, and only the person holding the private key can unlock it.
The question we hear most often is not “what is homomorphic encryption.” It’s “how does anyone get useful insights out of data they can’t actually read.”
That confusion usually clears up fast once you see the mechanics in action, so this article walks through three real patterns organizations use today, then covers where fully homomorphic encryption (FHE) is already running in production across regulated industries.

What Is Homomorphic Encryption Actually Used For?
Before getting into the walkthroughs, it helps to know the three tiers of homomorphic encryption, since the examples below draw on different ones.
- Partially homomorphic encryption (PHE) supports one operation, either addition or multiplication, indefinitely.
- Somewhat homomorphic encryption (SHE) supports both operations, but only up to a fixed number of computations before the underlying noise makes decryption unreliable.
- Fully homomorphic encryption (FHE) supports unlimited additions and multiplications through a process called bootstrapping, which periodically refreshes the ciphertext and clears out accumulated noise.
FHE is the version that makes complex, real-world workloads like machine learning and multi-party analytics possible. Here, we’re focused on what it looks like in practice.
How Does Machine Learning Run on Encrypted Data?

Picture two people, Alice and Bob. Alice owns sensitive data and wants insights from it. Bob owns a machine learning model and runs a cloud service that scores data against that model.
Bob makes money every time someone uses his service, so he has no intention of handing over the model itself.
Alice encrypts her data with her own key before sending it anywhere. Bob never sees it in plain form. Using Alice’s public evaluation key, he runs his model directly on the encrypted input and sends back an encrypted result.
Alice decrypts that result with her private key and gets her answer. Bob never learns what her data contained, and Alice never learns how his model works internally. Neither side has to trust the other with their assets.
This pattern is usually built on the CKKS scheme (approximate arithmetic scheme), since CKKS handles the kind of approximate, floating point arithmetic that machine learning models rely on. It’s also not theoretical.

Duality has published large scale, real world work applying exactly this approach to genome wide association studies, where research institutions need to run statistical models on genetic data without ever exposing individual genomes. You can see the details in our PNAS paper.
H2 How Does Private Information Retrieval Keep a Search Private?
Here’s a different problem. Alice is an investor who wants the current price of one specific stock.
Bob runs a public website listing every stock and its price. Alice can search his site directly, but then Bob knows exactly which stock she’s watching, which might tip him off to her trading strategy. She could download his entire database instead to keep her query private, but doing that every time a price changes gets expensive fast.
Homomorphic encryption solves this through a technique called private information retrieval, or PIR.
Bob assigns a number to every stock in his database. Alice encrypts the position she wants as a vector, essentially a list of zeros with a single one marking her stock. She sends that encrypted vector to Bob.
Using her public evaluation key, Bob multiplies the encrypted vector against his full price list and adds the results together, all without ever decrypting anything.
What comes back is the encrypted price for Alice’s chosen stock, and Bob genuinely cannot tell which entry she asked for. Every encrypted value looks identical to him, whether it represents a zero or a one.
This same pattern shows up outside of finance. Contact discovery and credential checking features on major platforms use closely related private set intersection techniques so a service can check whether a value is in a private list, without ever learning the value or exposing the full list.
If you want to dig into cryptography, Microsoft’s research paper and SealPIR project are good starting points.
For more advanced encrypted SQL style querying, our own Secure Query product handles this at enterprise scale.
How Can Multiple Organizations Combine Data Without Sharing It?
Now add more people to the picture. Alice, Bob, and Charles each run a hospital, and each holds patient records for their own facility. Individually, none of them has enough data to train an accurate model predicting a particular disease.
Pooling their data would fix that, but patient privacy laws and plain common sense rule out simply handing records to each other.
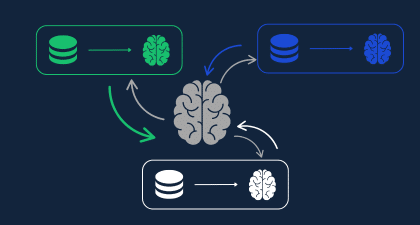
The fix combines homomorphic encryption with secret sharing, creating what’s known as multiparty homomorphic encryption. Alice, Bob, and Charles interactively generate a joint public key together, and critically, none of them ever holds the full private key on their own.
Each encrypts their own patient data with that shared key and sends it to Daisy, who trains a model on the combined encrypted data set.
Daisy sends the encrypted model back, and Alice, Bob, and Charles each compute a partial decryption using their own share of the key. Only when they combine those partial decryptions does the model become readable, and at no point does any single party see another’s raw patient records.
One caution worth flagging here. The insight itself needs to be chosen carefully so it doesn’t leak information indirectly. If the output is something like the average patient age, Alice and Bob could combine what they know to work out Charles’s average, even without ever seeing his data directly.
Pairing multiparty homomorphic encryption with differential privacy closes that gap. If you want the technical walkthrough in C++, our OpenFHE webinar covers implementation.

H2 Where Is Homomorphic Encryption Already Running in Production?
The three examples above are patterns. Here’s where those patterns are actually deployed today, outside of hypothetical Alice and Bob scenarios.
- Government and defense – Agencies that need to cross-reference intelligence or investigative data across departments, or even across countries, without exposing sources and methods, use encrypted computation to run zero footprint investigations. The data never leaves its original system in readable form. Duality’s zero footprint investigations and cross domain data collaboration work covers this directly.
- Cross-border health research – NHS England’s National Disease Registration Service and the US National Cancer Institute studied ultra-rare childhood tumors across both countries in a pilot run with the UK Department for Science, Innovation and Technology, using the Duality platform. No records were pooled. Approved scripts ran inside each organization’s own firewall and returned only site-level aggregates; a secure enclave combined them, so neither side saw the other’s raw numbers, with differential privacy noise and suppression of any result covering fewer than five patients. Researchers completed more than 450 queries on incidence, survival and demographic patterns, and analysis timelines fell 91 percent — from 23 months to about two.
- Insurance – Claims processing and underwriting both depend on data spread across insurers, reinsurers, and regulators. Encrypted computation lets these parties run joint risk models and fraud checks without any one party gaining visibility into another’s full book of business. See our claims processing use case for specifics.
- Manufacturing – Predictive maintenance models get better with more data, but suppliers and manufacturers are understandably reluctant to expose proprietary sensor readings or production data to each other. Homomorphic encryption lets them train shared models across the supply chain while keeping each party’s data walled off. Our predictive maintenance page has more detail.
What ties these four together is not the industry, it’s the same underlying problem. Each of these organizations needs to compute on data it cannot legally or contractually see in full.
Duality’s platform is built specifically for that problem. Instead of your team spending months implementing encryption schemes, managing keys, and tuning performance from scratch, Duality gives you that infrastructure ready to go, the same technology behind Secure Query, Secure Collaborative AI, and Federated Learning covered above. You bring the use case, Duality brings a working deployment.